A Comprehensive Guide to Building a CI/CD Pipeline with AWS Services in 2026
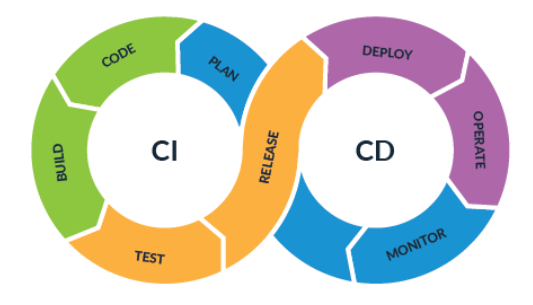
As software development practices continue to evolve, automating the build, test, and deployment processes has become essential for teams looking to deliver new features and updates quickly and reliably. Continuous Integration and Continuous Delivery, commonly known as CI/CD, is a set of practices that enable development teams to integrate code changes frequently, test them automatically, and deploy the updated application seamlessly.
In this step-by-step guide, we will walk through the process of setting up a robust CI/CD pipeline using AWS services such as CodeCommit, CodeBuild, CodePipeline, Elastic Container Service (ECS), and Fargate. By the end of this article, you will have a solid understanding of how to automate your application deployment workflow on AWS.
The Benefits of Implementing a CI/CD Pipeline
Before diving into the technical details, let‘s quickly review some of the key advantages of adopting a CI/CD approach:
-
Faster time-to-market: Automating the build, test, and deployment processes allows teams to release new features and bug fixes more frequently, reducing the time it takes to get updates into the hands of users.
-
Improved code quality: With automated testing integrated into the pipeline, potential issues can be caught early, ensuring that only high-quality code is deployed to production.
-
Increased efficiency: By eliminating manual steps and reducing the risk of human error, CI/CD pipelines streamline the deployment process, allowing developers to focus on writing code rather than managing infrastructure.
-
Better collaboration: CI/CD encourages a culture of continuous integration, where developers regularly merge their changes into a shared repository. This promotes collaboration and reduces the likelihood of merge conflicts.
Now that we understand the benefits, let‘s start building our CI/CD pipeline using AWS services.
Step 1: Create an Application Load Balancer
To ensure that our application is scalable and highly available, we‘ll start by creating an Application Load Balancer (ALB) in AWS. Follow these steps:
- Open the AWS Management Console and navigate to the EC2 service.
- In the left sidebar, click on "Load Balancers" and then click the "Create Load Balancer" button.
- Choose "Application Load Balancer" and click "Create."
- Configure the ALB by providing a name, selecting the desired VPC and availability zones, and clicking "Next."
- Create a new security group for the ALB, allowing inbound traffic on the necessary ports (e.g., HTTP/HTTPS).
- Configure the routing by creating a new target group and specifying the target type as "IP."
- Review the settings and click "Create" to provision the ALB.
Once the ALB is created, take note of its DNS name, as this will be the public endpoint for accessing your application.
Step 2: Set Up Fargate Task Definition and Service
Next, we‘ll create a task definition and service in ECS using Fargate, which allows us to run containers without managing the underlying infrastructure. If you‘re new to ECS and Fargate, refer to the AWS documentation for a more detailed explanation of these concepts.
- Open the ECS console and click on "Task Definitions" in the left sidebar.
- Click "Create new Task Definition" and choose "Fargate" as the launch type.
- Provide a name for the task definition and configure the container details, such as the image, port mappings, and environment variables.
- Set the task size by specifying the desired CPU and memory values.
- Review the settings and click "Create" to save the task definition.
With the task definition in place, we can now create a Fargate service:
- In the ECS console, click on "Clusters" and then "Create Cluster."
- Choose "Networking only" as the cluster template and provide a name for the cluster.
- Once the cluster is created, click on "Services" and then "Create."
- Select the previously created task definition and configure the service details, such as the desired number of tasks and deployment type.
- In the "Load balancing" section, choose "Application Load Balancer" and select the ALB and target group created in Step 1.
- Configure the networking by selecting the appropriate subnets and security groups.
- Review the settings and click "Create Service" to deploy the Fargate service.
At this point, your application should be running and accessible via the ALB‘s DNS name. However, to enable automated deployments, we‘ll need to set up the CI/CD pipeline.
Step 3: Create a CodeCommit Repository
AWS CodeCommit is a fully-managed source control service that hosts private Git repositories. We‘ll use CodeCommit to store our application code and trigger the CI/CD pipeline whenever changes are pushed.
- Open the CodeCommit console and click "Create repository."
- Provide a name for the repository and click "Create."
- Follow the instructions to configure your local Git environment to access the CodeCommit repository.
To allow CodeCommit to interact with other AWS services, we‘ll need to set up the necessary IAM permissions:
- Open the IAM console and navigate to "Users."
- Select the user that will be accessing CodeCommit and click on "Add permissions."
- Attach the "AWSCodeCommitPowerUser" policy to grant the required permissions.
- Generate Git credentials for the user to authenticate with CodeCommit.
Step 4: Push Application Code to CodeCommit
With the CodeCommit repository set up, you can now push your application code to it:
- Clone the empty repository to your local machine using the Git credentials generated in the previous step.
- Copy your application code into the cloned repository.
- Stage and commit the changes using the following commands:
git add .
git commit -m "Initial commit"- Push the changes to the CodeCommit repository:
git push -u origin masterYour application code is now stored in CodeCommit and ready to be built and deployed.
Step 5: Set Up CodeBuild Project
AWS CodeBuild is a fully managed continuous integration service that compiles source code, runs tests, and produces deployment-ready artifacts. We‘ll use CodeBuild to build and package our application.
- Open the CodeBuild console and click "Create project."
- Provide a name for the project and choose the CodeCommit repository as the source.
- Configure the build environment by selecting the appropriate operating system, runtime, and image.
- Specify the buildspec file, which contains the build commands. We‘ll create this file in the next step.
- Set up any necessary environment variables, such as AWS credentials or application-specific configurations.
- Review the settings and click "Create build project."
Next, create a buildspec.yml file in the root directory of your application code. This file specifies the build commands and artifacts to be generated. Here‘s an example buildspec file for a containerized application:
version: 0.2

phases:
  pre_build:
    commands:
      - echo Logging in to Amazon ECR...
      - aws ecr get-login-password --region $AWS_DEFAULT_REGION | docker login --username AWS --password-stdin $AWS_ACCOUNT_ID.dkr.ecr.$AWS_DEFAULT_REGION.amazonaws.com
  build:
    commands:
      - echo Building the Docker image...
      - docker build -t $IMAGE_REPO_NAME:$CODEBUILD_RESOLVED_SOURCE_VERSION .
      - docker tag $IMAGE_REPO_NAME:$CODEBUILD_RESOLVED_SOURCE_VERSION $AWS_ACCOUNT_ID.dkr.ecr.$AWS_DEFAULT_REGION.amazonaws.com/$IMAGE_REPO_NAME:$CODEBUILD_RESOLVED_SOURCE_VERSION
  post_build:
    commands:
      - echo Pushing the Docker image...
      - docker push $AWS_ACCOUNT_ID.dkr.ecr.$AWS_DEFAULT_REGION.amazonaws.com/$IMAGE_REPO_NAME:$CODEBUILD_RESOLVED_SOURCE_VERSION
      - printf ‘[{"name":"%s","imageUri":"%s"}]‘ "$CONTAINER_NAME" "$AWS_ACCOUNT_ID.dkr.ecr.$AWS_DEFAULT_REGION.amazonaws.com/$IMAGE_REPO_NAME:$CODEBUILD_RESOLVED_SOURCE_VERSION" > imagedefinitions.json
artifacts:
  files: imagedefinitions.json
This buildspec file logs in to Amazon ECR, builds the Docker image, tags it with the current commit ID, pushes the image to ECR, and generates an imagedefinitions.json file containing the updated image URI. The imagedefinitions.json file will be used by CodePipeline to update the Fargate service with the new image.
Remember to replace the placeholders ($AWS_ACCOUNT_ID, $IMAGE_REPO_NAME, $CONTAINER_NAME) with your actual values.
Step 6: Configure CodePipeline
AWS CodePipeline is a fully managed continuous delivery service that automates the release process, from code changes to production deployment. We‘ll use CodePipeline to orchestrate the CI/CD workflow.
- Open the CodePipeline console and click "Create pipeline."
- Provide a name for the pipeline and choose "New service role" to create an IAM role for CodePipeline.
- In the "Source" stage, select CodeCommit as the source provider and choose the repository and branch.
- In the "Build" stage, select CodeBuild as the build provider and choose the project created in Step 5.
- In the "Deploy" stage, select Amazon ECS as the deployment provider and configure the following:
- Cluster: Choose the Fargate cluster created in Step 2.
- Service name: Choose the Fargate service created in Step 2.
- Image filename: Specify the path to the
imagedefinitions.jsonfile generated by CodeBuild (imagedefinitions.jsonin our example).
- Review the settings and click "Create pipeline."
CodePipeline will now automatically trigger the CI/CD process whenever changes are pushed to the specified CodeCommit repository branch.
Step 7: Test the CI/CD Pipeline
To verify that the CI/CD pipeline is working as expected, make a change to your application code and push the changes to the CodeCommit repository:
- Modify a file in your local repository.
- Stage and commit the changes:
git add .
git commit -m "Update application"- Push the changes to CodeCommit:
git push origin masterCodePipeline will detect the changes and start the automated build and deployment process. You can monitor the progress in the CodePipeline console.
Once the pipeline execution is complete, access your application using the ALB‘s DNS name to verify that the changes have been deployed successfully.
Best Practices and Tips
Here are some best practices and tips to keep in mind when working with CI/CD pipelines on AWS:
-
Secure your pipeline: Ensure that your AWS resources, such as CodeCommit repositories and ECS clusters, are properly secured with appropriate IAM roles and policies. Regularly review and update access permissions to maintain the principle of least privilege.
-
Use separate AWS accounts: Consider using separate AWS accounts for different environments (e.g., development, staging, production) to isolate resources and minimize the impact of potential issues.
-
Monitor and log pipeline events: Utilize AWS services like CloudWatch and CloudTrail to monitor your CI/CD pipeline and log important events. Set up alerts to notify you of any failures or anomalies.
-
Implement testing: Incorporate automated testing into your CI/CD pipeline to catch bugs and ensure the quality of your application. You can use tools like AWS CodeBuild or third-party testing frameworks to run unit tests, integration tests, and end-to-end tests.
-
Manage secrets securely: Store sensitive information, such as database credentials or API keys, using secure services like AWS Secrets Manager or AWS Systems Manager Parameter Store. Avoid hardcoding secrets in your application code or buildspec files.
-
Regularly update dependencies: Keep your application dependencies up to date to ensure compatibility and security. Use tools like dependabot or AWS CodeArtifact to automate dependency updates and vulnerability scanning.
Cleaning Up AWS Resources
When you‘re done experimenting with the CI/CD pipeline, make sure to clean up the AWS resources to avoid unnecessary costs:
- Delete the Fargate service and cluster from the ECS console.
- Delete the CodePipeline pipeline from the CodePipeline console.
- Delete the CodeBuild project from the CodeBuild console.
- Delete the CodeCommit repository from the CodeCommit console.
- Delete the Application Load Balancer and target group from the EC2 console.
- Remove any IAM roles and policies created specifically for this setup.
Conclusion
In this comprehensive guide, we walked through the process of building a CI/CD pipeline using AWS services. By leveraging CodeCommit, CodeBuild, CodePipeline, ECS, and Fargate, we automated the build, test, and deployment processes, enabling faster and more reliable application updates.
Remember, a well-designed CI/CD pipeline is an essential component of modern software development practices. It allows teams to deliver value to users more quickly, reduce the risk of errors, and foster a culture of continuous improvement.
As you continue to refine your CI/CD pipeline, consider exploring additional AWS services and features, such as AWS CodeStar for end-to-end project management, AWS CodeDeploy for application deployments, and AWS Lambda for serverless computing.
By mastering the art of CI/CD on AWS, you‘ll be well-equipped to build and deploy applications with confidence, speed, and scalability.
Happy automating!